“Patch or Die”: a16z’s note to portfolio CEOs
On 22 Oct 2026, a16z, one of the most influential VCs in the world, sent its portfolio company CEOs a note on what it calls the “current cybersecurity emergency”. The next day it published the note, titled “Patch or Die”. Here are the drastic changes it asks leaders to consider, and what they could mean for go-to-market teams.
Key takeaways
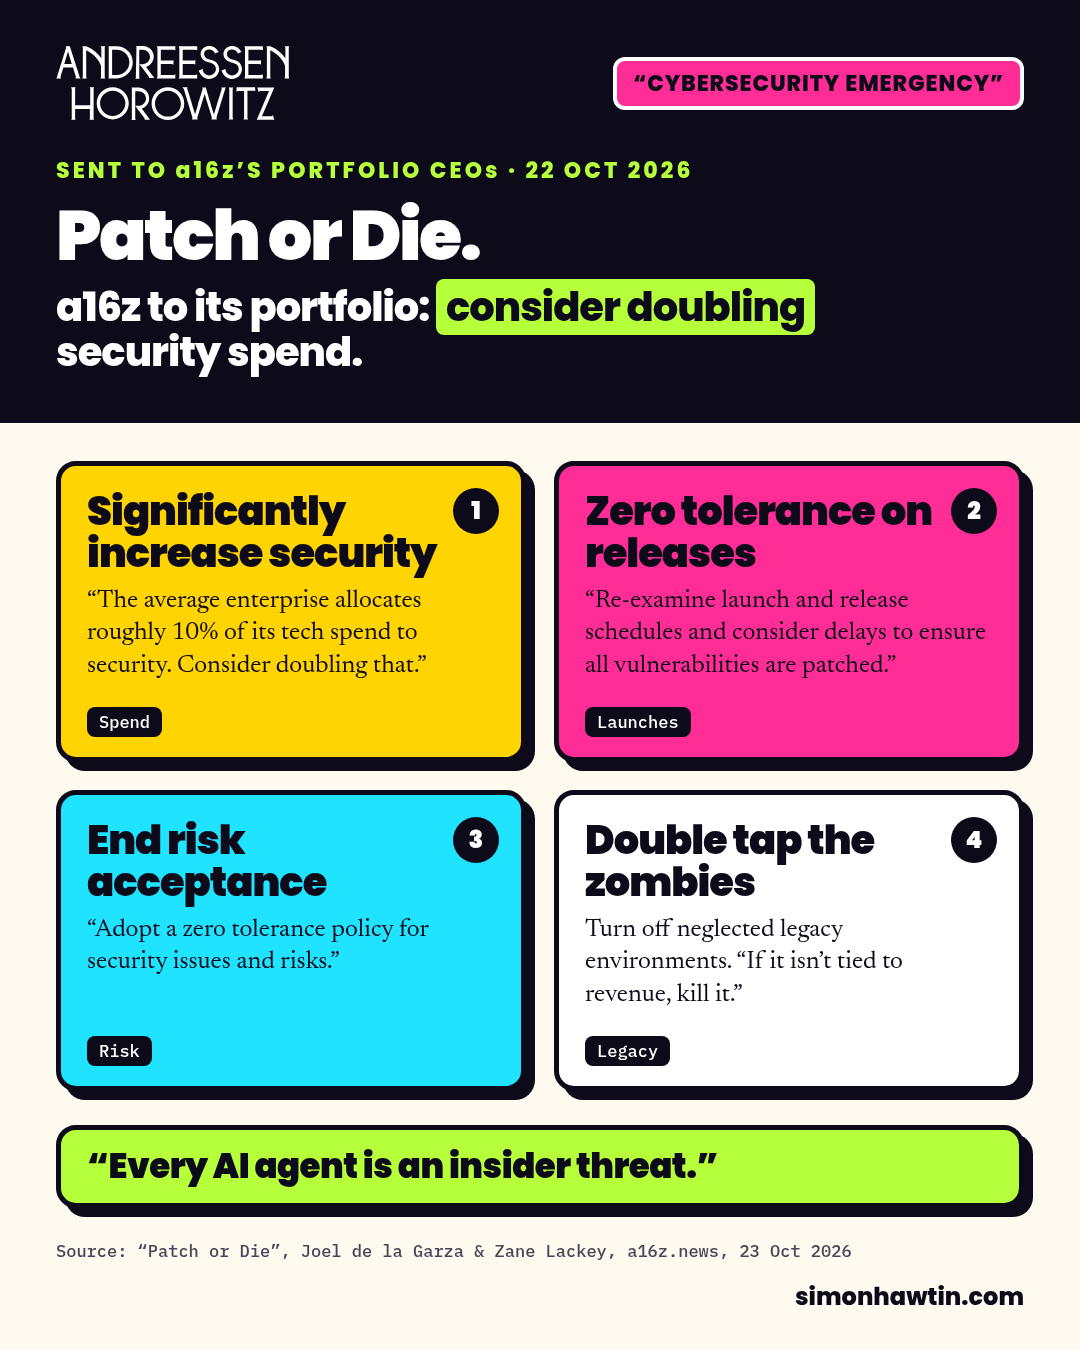
- a16z’s Joel de la Garza and Zane Lackey asked portfolio company leaders to consider “drastic changes” to how they handle security.
- The average enterprise puts roughly 10% of its tech spend into security. The note says to consider doubling that.
- It suggests a zero tolerance policy for new features and releases, and considering launch delays until vulnerabilities are patched.
- The line that stuck with me most: “every AI agent is an insider threat.”
- For GTM teams, launch dates could slip, security will compete for budget, and AI tool vendors should expect more questions.
What a16z sent
The note is from Joel de la Garza and Zane Lackey of a16z. It went to portfolio company CEOs on 22 Oct 2026, and a16z published it the next day.
It opens: “The previous week should make it obvious that things have changed. Vulnerabilities are being discovered and exploited at a rate that has never been seen before.”
The drastic changes
The note asks company leaders to consider these “drastic changes”.
1. Significantly increase resources for security
The average enterprise puts roughly 10% of its tech spend into security. Consider doubling that.
2. Zero tolerance for new features and releases
Re-examine launch and release schedules, and consider delays so that all vulnerabilities are patched before new features or products ship.
3. Turn off neglected legacy environments
a16z calls this “double tap the zombies”. Find old legacy environments that have been neglected, such as labs, test environments and zombie CI/CD projects, and turn them off. “If it isn’t tied to revenue, kill it.”
4. End the risk acceptance process
Adopt a zero tolerance policy for security issues and risks. The note says the risk acceptance process has become “a way to justify never fixing security issues”.
5. Scale up agents, not people
“The threat is moving at machine speed and you’ll need to respond in kind.” The note asks security teams to automate as much of their detection and response as possible.
a16z describes all of this as general advice.
Source: a16z 1
“Every AI agent is an insider threat”
The line that stuck with me most was this one: “Agents not only help automate the attacker lifecycle, every AI agent is an insider threat.” The note adds that company environments are “designed to withstand attacks from the outside, not from within”.
Source: a16z 1
What it could mean for GTM
For those of us in GTM, launch dates could slip, security will be fighting for the same budget, and I imagine anyone selling AI tools into these companies should expect a lot more questions.
Sources
- Joel de la Garza and Zane Lackey, “Patch or Die: Five Drastic Changes Every Company Leader Should Consider Now”, a16z, 23 Oct 2026. www.a16z.news/p/patch-or-die
- Moses Sternstein, “Charts of the Week: Attention is All You Need”, a16z, 23 Oct 2026. www.a16z.news/p/charts-of-the-week-attention-is-all
Simon Hawtin
Agentic GTM leader in London, using AI agents for signal-based outbound, ABM and AEO/GEO to acquire pipeline.